
Examining Vulnerabilities in Meta’s Ray-Ban Smart Glasses
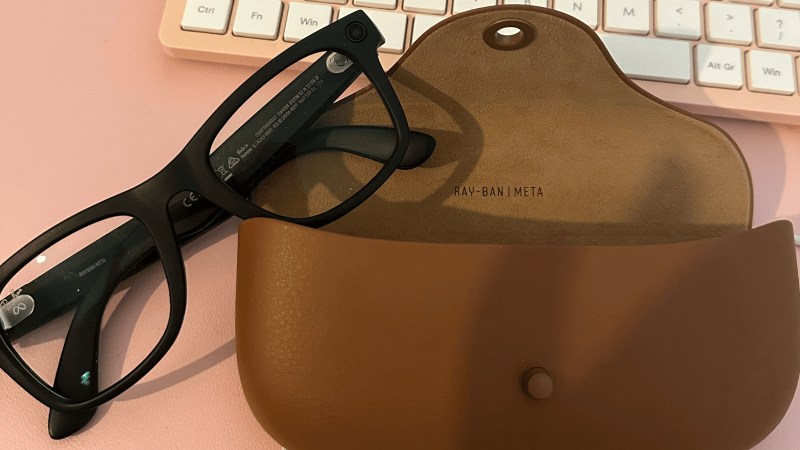
Meta’s Ray-Ban smart glasses have sparked significant controversy since their launch, primarily due to concerns about their potential for covert surveillance. Recently, an opportunity arose for a detailed examination of the device’s defenses.
The examination was conducted by a user known as p0pcycle, who opted to intercept a software update instead of probing the hardware directly. Through decompiling an application, she accessed the full firmware of the glasses.
During her investigation, p0pcycle discovered a developer mode that permits the creation of applications for the glasses, utilizing an APK format to load application code. An earlier firmware version had a security flaw that allowed self-signed apps to be trusted, enabling her to run arbitrary code on the device.
After some experimentation, she successfully exposed a network listener, revealing critical information about the device’s operations. The detailed write-up of her process concluded with her reporting the vulnerabilities through Meta’s bug bounty program.
While the methods she used may no longer be effective on newer firmware versions, it is likely that others will continue to explore the security of this device.
Source: Hackaday